Vendor-agnostic advisory · IAM Advisory
Make identity the strongest part of your security program.
Advisory for the identity program you run today: workforce, customer, privileged, and non-human identity. We work with the platforms you already have, whichever vendors they are, and stay through the decisions that matter.
For CISOs, IAM leaders, identity architects, PAM and IGA leaders, and CIOs.
Who leads the work
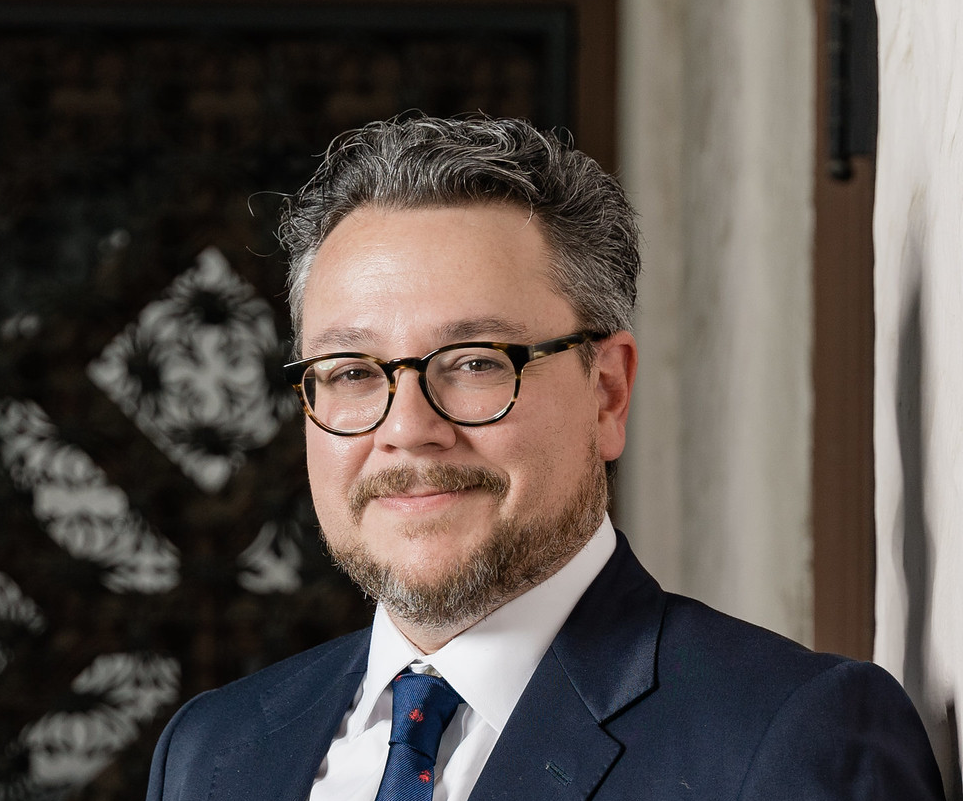
Led by Aldo Pietropaolo, a security and identity executive with 25+ years of experience, including Field CTO and solutions leadership roles at Strata Identity and SGNL.
Aldo advises IAM, security, and AI platform teams on identity programs, agent identity, delegated authority, and runtime control.
Strata Identity
Field CTO
Identity orchestration for enterprises across North America, EMEA, and APAC.
SGNL
Director of Solutions Engineering
Continuous access management for APIs, data, and applications.
PwC
Manager, CIO Advisory
IAM strategy and security governance assessments for financial services and insurance.
HP
Identity and security subject matter expert
HP Software strategic pre-sales.
RSA Security
Technical Manager, Identity & Access Management
Access management for large e-commerce environments.
Also ran a large IAM services practice, co-founded and sold an IAM company, and created Agent Runtime Governance and its 12 Principles.
Full backgroundWhen teams call us
Where identity programs get stuck
Attackers often log in instead of breaking in: a stolen session, a reset password, a privileged account left open. These are the moments that usually bring a team to us.
- Identity platforms bought, but coverage and adoption behind the plan
- Access reviews that get rubber-stamped, and entitlements nobody can explain
- A help desk or account recovery process an attacker could talk their way through
- Privileged and service accounts that hold standing access
- An audit finding, a merger, or a new CISO asking where identity stands
- Non-human identities, including AI agents, arriving faster than the policy for them
The engagements
Each one stands on its own. Scope, timing, and investment are agreed up front for your environment.
IAM Program Assessment and Roadmap
Typically 3 to 4 weeks
Where your identity program stands across workforce, customer, privileged, and non-human identity, measured against your goals and risks, with a roadmap your team can act on.
What you leave with
- Current-state and maturity assessment
- Risk-ranked gaps
- A 12 to 18 month roadmap with sequencing and owners
- Executive readout
Agent Identity Exposure Review
Typically 1 to 2 weeks
The AI agents your identity program can’t see yet: which agents run, whose access they use (a person’s token, a shared service account, an API key), who owns each one, and which IAM, PAM, and IGA controls cover them.
What you leave with
- Inventory of agents and the identities they act through
- Credential and ownership map
- Coverage gaps against your IAM, PAM, and IGA controls
- The riskiest agents first, and whether a deeper design is the next step
Identity Platform Strategy and Selection
Scoped to the decision
Requirements and an independent evaluation for identity, PAM, or IGA platforms, and the plan to consolidate or migrate without breaking access.
What you leave with
- Requirements and evaluation criteria
- Scored comparison and recommendation
- Consolidation or migration plan
- Cutover risks and how to manage them
Identity Attack Resilience
Scoped to your environment
Close the paths attackers use to take over accounts: help desk and account recovery, gaps in MFA, session and token theft, and privileged access.
What you leave with
- Identity attack-path review
- Help desk and recovery verification design
- Phishing-resistant MFA plan
- Prioritized fixes
PAM and IGA Program Design
Scoped to your environment
Privileged access and identity governance that hold up: just-in-time access, joiner-mover-leaver, access reviews people take seriously, and entitlement cleanup.
What you leave with
- Target operating model
- Plan to reduce standing privilege
- Access review and certification design
- Role and entitlement approach
Fractional IAM Leadership
Monthly, a set number of days
A senior identity leader working with your team: program direction, architecture review, vendor and board conversations, and mentoring for the people who run identity day to day.
What you leave with
- A named senior identity advisor
- Program oversight and decision support
- Architecture and design reviews
- Board and audit preparation
When AI agents start acting for your people
Agents are the newest non-human identities, and the first that make decisions. Most of them run on borrowed access today. Start with an Agent Identity Exposure Review to see where they stand; Agentic IAM Architecture then extends the same identity program to agent identity, credentials, lifecycle, and delegated authority.
Vendor agnostic
We have no platform to sell you for workforce, customer, privileged, or governance identity. The recommendations follow your requirements.
- Designed for the identity, PAM, and IGA platforms you already run, whichever vendors they are
- Platform evaluations scored against your requirements, with the trade-offs written down
- Built on open standards: SAML, OAuth 2.0, OIDC, SCIM, and FIDO2 where they apply
- No product purchase required, during or after the engagement
Disclosure: Watchlight also builds Watchlight AI Beacon, an Agent Runtime Governance product for AI agents. IAM Advisory does not require it, and we tell you plainly when another option fits better.
Questions from identity leaders
What does IAM Advisory cover?
Workforce, customer, privileged, and non-human identity. The engagements are an IAM program assessment and roadmap, an agent identity exposure review, identity platform strategy and selection, identity attack resilience, PAM and IGA program design, and fractional IAM leadership.
Do we need AI agents to work with you?
No. IAM Advisory is for the identity program you run today. When AI agents arrive, Agentic IAM Architecture extends the same program to agent identity, credentials, and delegated authority.
How long does an IAM program assessment take?
Typically 3 to 4 weeks. It ends with a current-state and maturity assessment, risk-ranked gaps, a 12 to 18 month roadmap with sequencing and owners, and an executive readout.
What is an Agent Identity Exposure Review?
A short review, typically 1 to 2 weeks, of the AI agents already running in your environment and the identities they act through: a person’s token, a shared service account, or an API key. You leave with an inventory, a credential and ownership map, the gaps against your IAM, PAM, and IGA controls, the riskiest agents first, and a recommendation on whether Agentic IAM Architecture is the next step.
Is the advice vendor agnostic?
Yes. We work with the identity, PAM, and IGA platforms you already run, whichever vendors they are, and score platform options against your requirements with the trade-offs written down. No product purchase is required. Watchlight also builds Watchlight AI Beacon for AI agents; IAM Advisory does not require it.
What is fractional IAM leadership?
A senior identity leader working with your team for a set number of days each month: program direction, architecture and design reviews, vendor and board conversations, audit preparation, and mentoring for the people who run identity day to day.
Need a clear view of where identity stands?
Tell us about your program. We typically respond within one business day.